Run the Tabletop Exercise
Your Auditor Is Looking For
Satisfy SOC 2, ISO 27001, HIPAA, PCI DSS, and NYDFS incident response testing requirements in 90 minutes — with AI-powered scenarios and audit-ready reports you can drop straight into Thoropass.
Compliance-Ready Tabletop Exercises — Without the Overhead
Built for Thoropass customers who need to test their incident response plan to satisfy auditor requirements — without spending weeks on prep or five figures on a consultant.
Pass Your Audit
Generate the IR testing evidence your auditor expects — control-mapped, timestamped, and ready to upload to Thoropass.
Skip the Consultant
Replace the $15K+ annual tabletop with AI-driven scenarios you can run in 90 minutes — and rerun anytime.
Actually Get Better
Most tabletops are check-the-box theater. Ours surface real gaps, track them across runs, and show measurable year-over-year improvement.
One Exercise. Evidence for Every Framework.
Nearly every major security and privacy framework requires you to test your incident response plan — at least annually, with documented evidence. A single ChaosTrack tabletop produces a report mapped to the controls below.
CC7.3 / CC7.4 — Incident response testing
A.5.24 — Incident management planning & testing
§164.308(a)(7) — Contingency plan testing & revision
Req. 12.10.2 — Annual IR plan review & testing
§500.16 — Incident response plan testing
RS.MA / RC.RP — Response & recovery exercises
IR-3 — Incident response testing
IR.L2-3.6.3 — Test IR capability
Realistic Scenarios —
Not Generic Templates
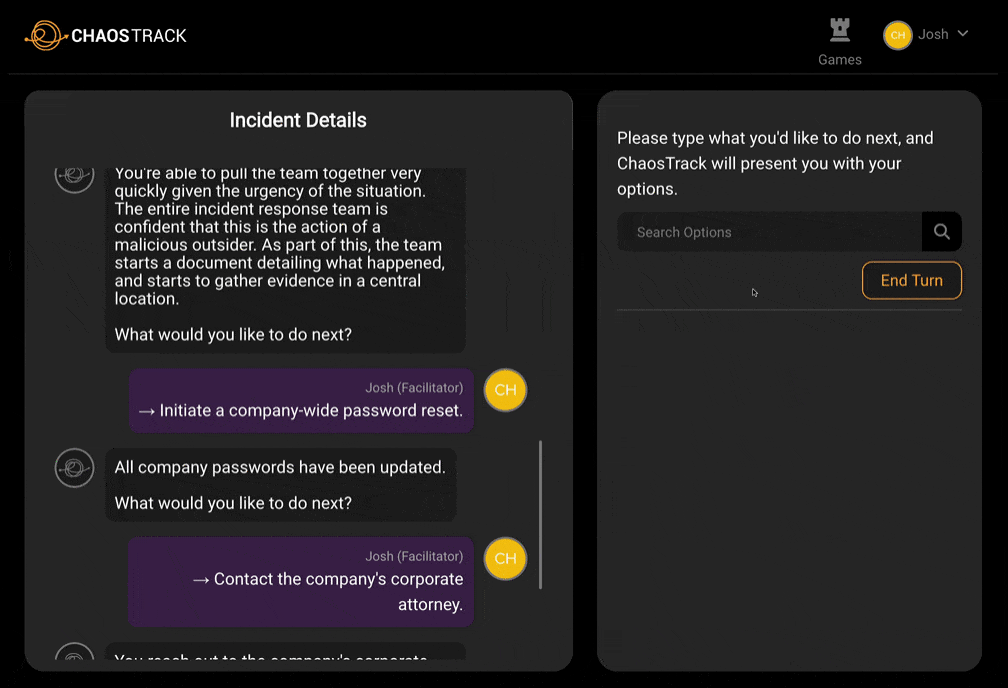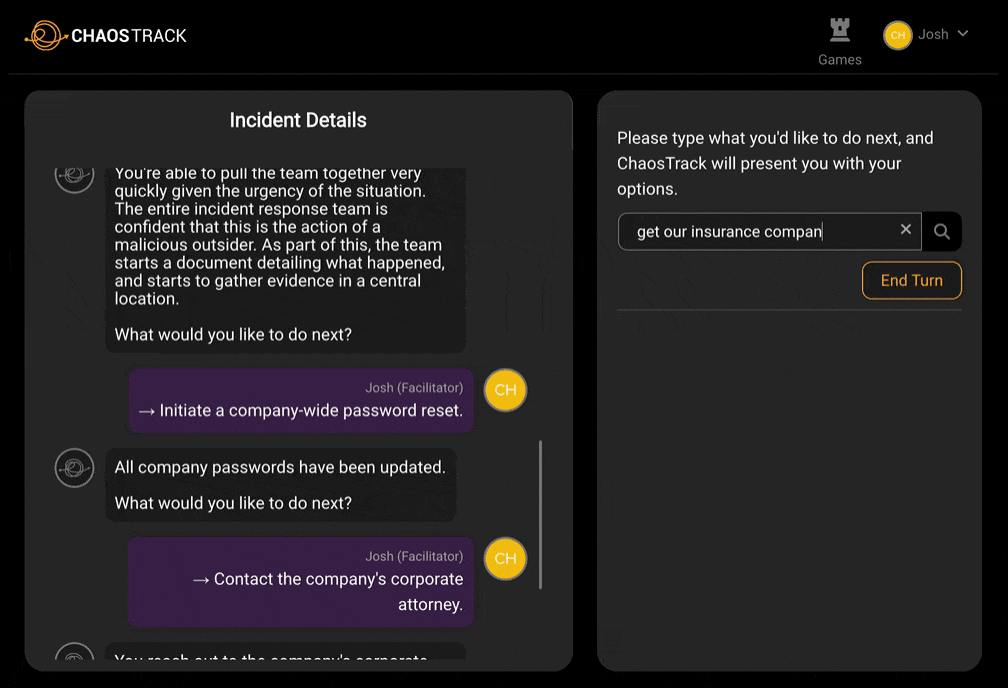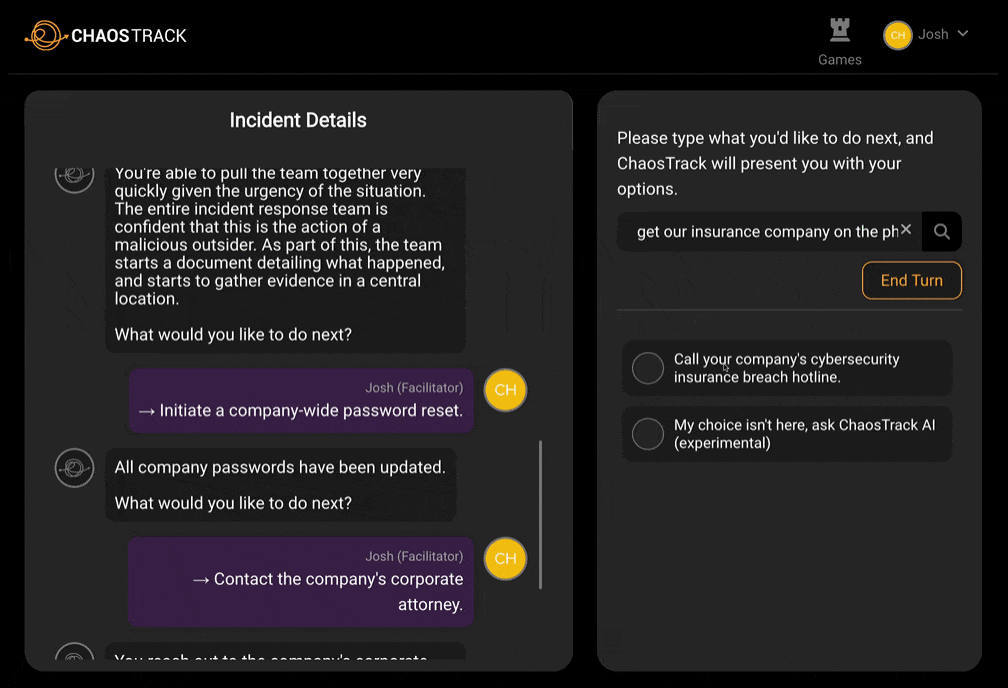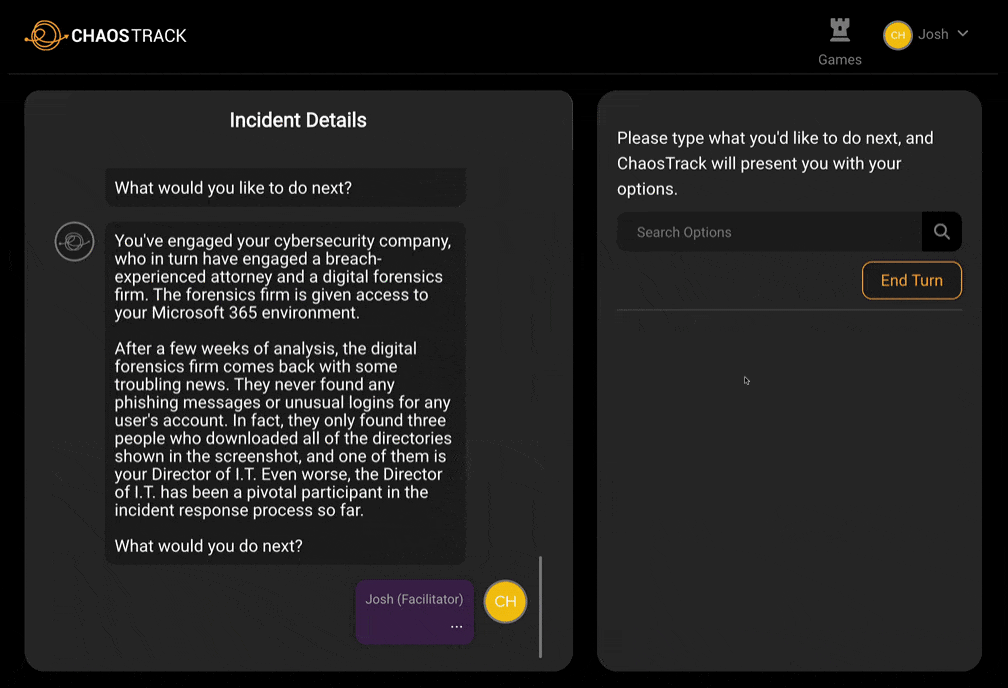
Ransomware, business email compromise, third-party vendor breach, data exfiltration — every scenario is tailored to your stack and team. Participants join live or async from any device, and the AI adapts in real time based on their decisions. The result: an exercise auditors find credible and your team actually finds useful.
Audit-Ready Reports.
Upload Straight to Thoropass.
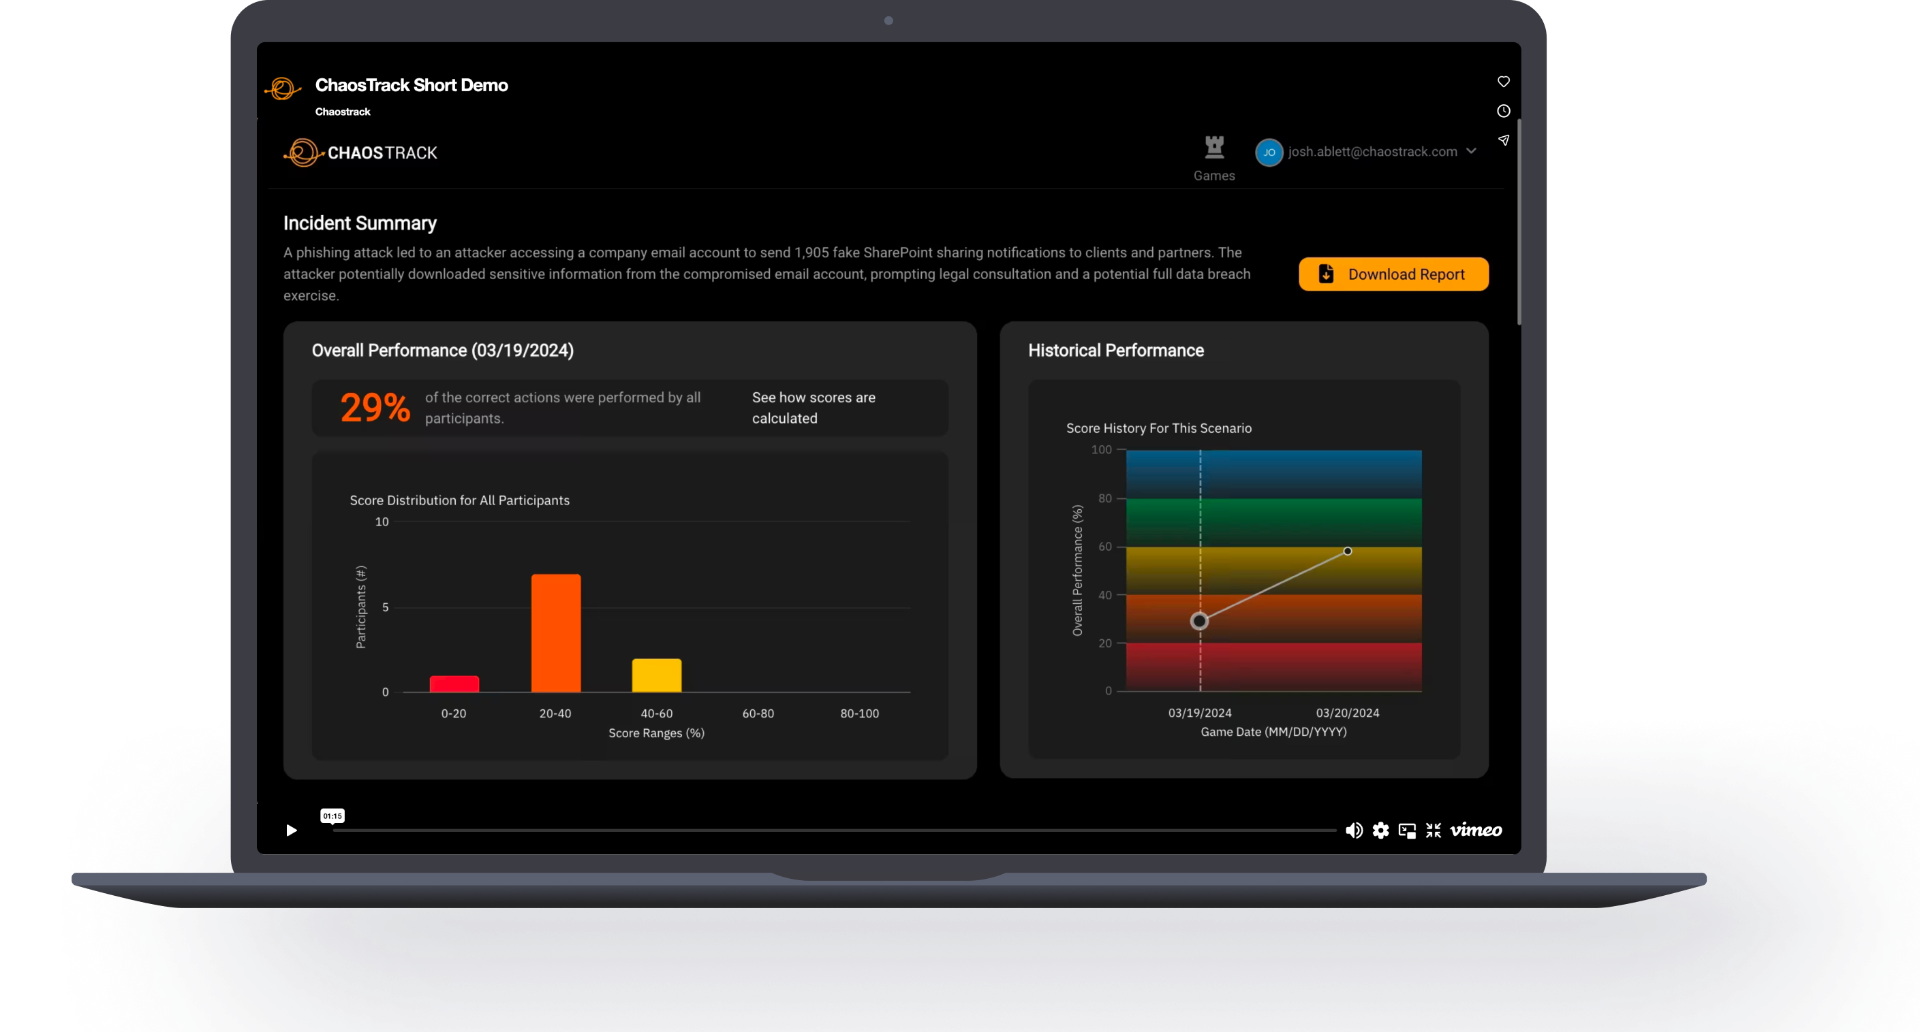
Every exercise generates a structured PDF with scenario, attendees, decisions, identified gaps, and remediation actions — mapped to SOC 2, ISO 27001, HIPAA, PCI, and NYDFS controls.
Drop it into your Thoropass workspace as IR testing evidence. Next year, rerun the same scenario and show your auditor measurable improvement.
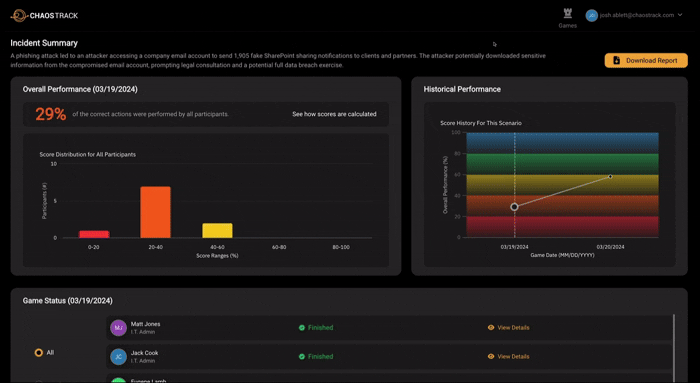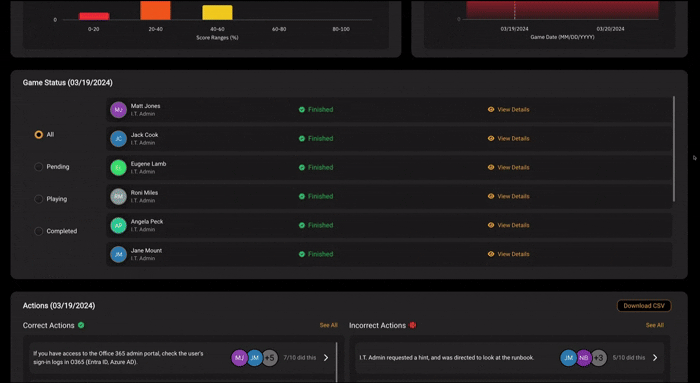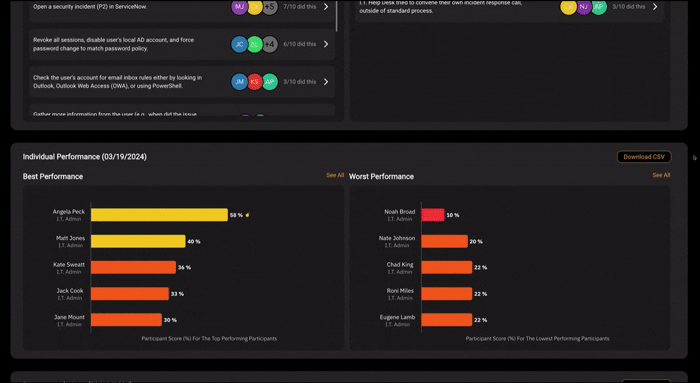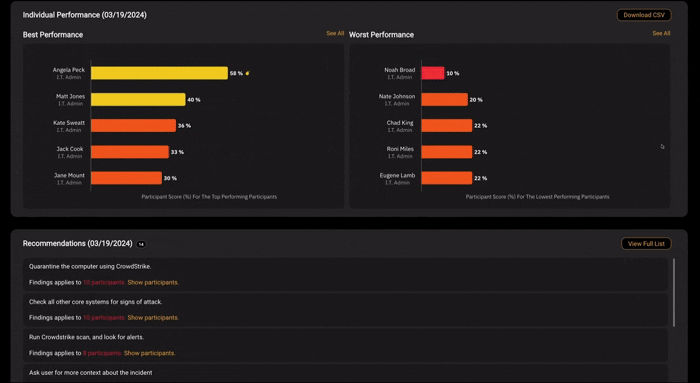
From Kickoff to Audit Evidence in 90 Minutes

1. Pick a Scenario
Choose from compliance-relevant scenarios — ransomware, BEC, vendor breach, data exfiltration — tailored to your environment.

2. Run the Exercise
Invite IT, security, legal, and leadership. Run live or async. ChaosTrack tracks every decision and timestamp.

3. Upload to Thoropass
Download the auto-generated, control-mapped report and drop it into your Thoropass workspace as IR testing evidence.
Frequently Asked Questions
Yes. Auditors expect documented evidence that your incident response plan is tested at least annually. ChaosTrack runs a realistic, role-based tabletop exercise tailored to your environment and automatically generates an audit-ready after-action report — covering scenario, participants, decisions, gaps, and remediation actions — that you can drop directly into Thoropass or your audit workspace.
Check the Box. Actually Get Ready.
Satisfy your IR testing requirement. Surface real gaps. Show year-over-year improvement.
Book a 20-minute demo and walk away with a clear plan to run your compliance tabletop in the next two weeks.